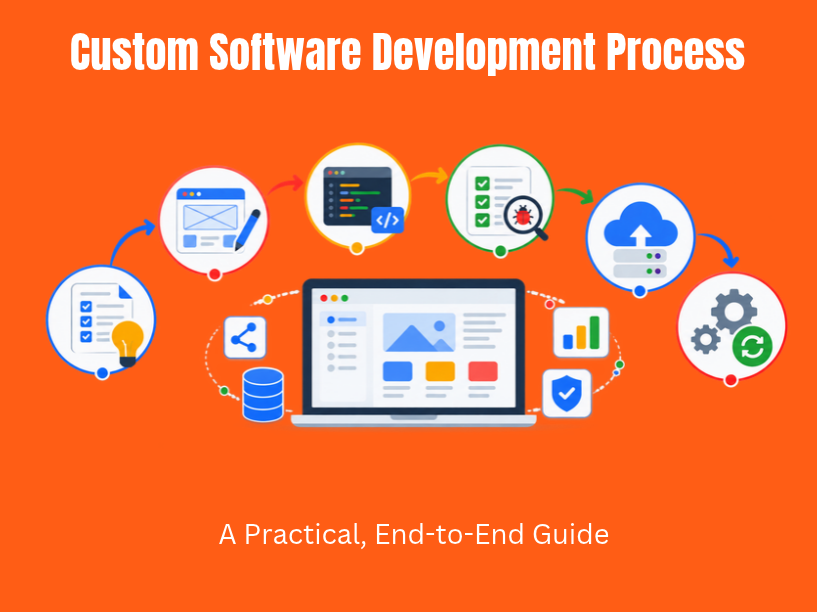

Building custom software is one of the highest-impact investments an organization can make. But the technology you choose matters far less than the process you follow to build it. Custom software development refers to the practice of designing, building, and maintaining applications tailored for specific organizational needs, as opposed to buying off the shelf software designed for general use.
Here is the reality: 45% of enterprise software projects exceed original timelines due to inadequate process discipline. Not because teams picked the wrong programming languages or cloud platforms, but because they skipped critical steps in the development process.
This guide walks through a practical, real-world software development lifecycle for building custom software – from the first idea through long-term evolution. It covers every phase that determines whether your custom software project ships on time or joins the 19% that get cancelled outright.
TVL IT Solutions, an India-based custom software development company and offshore partner, follows this disciplined, security-first process when delivering web, mobile, game, and enterprise solutions for clients across the globe.
What this article covers:
The custom software development process includes seven overlapping phases, and the core principles – clear business objectives, iterative delivery, continuous improvement – apply whether you are a startup or an enterprise.
Business objectives must be defined before discussing technology to prioritize outcomes over features. Before a single line of code gets written, the development team needs to understand what business problem the software solves and how success will be measured.
Start by translating high-level goals into actionable targets:
From these sessions, the team creates measurable success metrics: adoption targets, SLA benchmarks, compliance milestones. Features should be prioritized based on must-have, should-have, and nice-to-have classifications – a structure known as MoSCoW prioritization.
The output is an initial feature backlog grouped by themes such as “Order Management,” “Analytics,” “Integrations,” and “Security & Compliance.” This backlog becomes the living contract between business and engineering.
TVL IT Solutions facilitates these sessions remotely for offshore clients using tools like Miro, Jira, and Azure DevOps, keeping the backlog transparent and accessible across time zones. Custom software should be tailored to the vendor’s specific needs, and that alignment starts here. Clear scope and requirements prevent scope creep and miscommunication during a project. Effective custom software management balances business goals, technical quality, and team collaboration from the very first workshop.
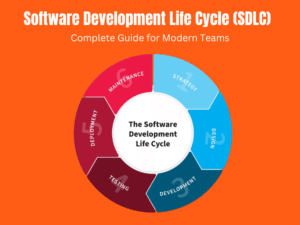
Custom software development follows the Software Development Life Cycle – a structured sequence of phases from idea through deployment and ongoing maintenance. But which model you use within that lifecycle determines how you handle risk, change, and delivery cadence.
The three main approaches:
Choosing a software development methodology is a strategic decision, not a preference. Adopting an iterative methodology allows teams to deliver updates frequently and adapt to feedback. But when regulatory milestones are immovable, a more structured gate is warranted.
Mini-scenario: For a new React Native mobile app, TVL IT Solutions typically uses Scrum with 2-week sprints. For a Microsoft Dynamics integration subject to SOX audits, they apply a hybrid approach – fixed compliance milestones with agile execution within each phase.
Proactive risk and change management addresses potential blockers and client priority shifts early in projects. Architecture and planning selects the technology stack, defines system architecture, and sets timelines or sprints. The model you choose shapes everything downstream.
The discovery phase is the foundation of any custom software development project. Requirements gathering typically spans two to four weeks in enterprise environments, though complex multi-region platforms with legacy systems can extend that timeline to several months.
Key activities include:
The deliverables from discovery include a discovery report with findings and assumptions, a risk register, a prioritized feature list, and initial architecture options comparing cloud-native versus on-premise and monolith versus microservices.
A concrete example: during discovery for a UK logistics company in 2024, the team found that existing software – specifically, spreadsheets used across teams – had deeply inconsistent data fields. Different departments used separate definitions for “delivery date.” Catching this data quality issue early prevented weeks of rework and avoided misaligned analytics outputs in the final platform.
Regular communication prevents small issues from becoming major delays in projects, and discovery is where that communication cadence gets established.
Requirements gathering bridges discovery and building. The goal is to refine discovery insights into structured artifacts – a software requirements specification, user stories, and acceptance criteria – that the development team can act on.
Methods that deliver results:
Requirements split into epics and user stories with a clear “Definition of Done” tied to business goals. A strong requirement looks like: “As a warehouse manager in 2026, I need to scan items with a mobile app so I can update inventory management systems within 5 seconds.” A vague one: “Needs fast inventory updates.”
Non-functional requirements deserve equal attention – performance targets, security standards, availability SLAs, and accessibility compliance. These are critical in tailored solutions intended for long-term scale.
User feedback aids in creating a user-centric software design. Throughout the project, TVL IT Solutions maintains a living backlog that evolves as the team learns more, avoiding static spec documents that quickly go stale. Maintaining living documentation aids in minimizing onboarding friction and managing project assets.
When requirements are written well, the entire software development process accelerates. When they are vague, every downstream phase pays the price.
Once requirements are clear, architects translate them into a technical blueprint covering system components, APIs, databases, and infrastructure choices. This is where the system architecture takes shape.
Key architectural decisions include:
Security-first development means conducting threat modeling, data classification, and defining encryption strategy before writing code. Custom software enhances security tailored to specific business needs, and that security starts at the architecture level.
Scalability allows software to handle increased user demands effectively. Scalable software future-proofs systems against changing business needs. Scalable systems support high availability and redundancy for reliability. Scalability optimizes resource utilization based on demand fluctuations.
Mini case study: A retail client chose a modular microservices architecture in 2023. By 2025, they plugged in AI-based product recommendations without rewriting core modules. That flexibility came directly from the technology stack decisions made during architecture.
Architecture defines the skeleton. Technical design fills in the details – screen flows, component diagrams, database schemas, API contracts, and the business logic layer.
On the UX side, the design phase produces UI/UX designs and technical documentation that ensure the interface supports real workflows rather than just looking polished:
Accessibility ensures equal opportunities for individuals with disabilities, and accessibility is often legally required for software applications. Incorporating accessibility features expands the user base significantly. Accessibility improvements enhance overall user experience for all users, not just those with disabilities. Accessibility considerations can future-proof software applications by staying ahead of evolving compliance requirements like WCAG.
Localization planning – supporting multiple languages and regional formats – is addressed here rather than retrofitted later.
TVL IT Solutions runs design validation sessions with actual users before committing to development. For a CRM project, sales reps tested a demo on their own phones, catching navigation issues that internal reviewers missed. Analyzing user behavior during these sessions reveals friction points that static reviews cannot surface.
With architecture and design established, the team turns the backlog into a realistic roadmap with phased releases: MVP, pilot, version 1.0, and later enhancements. Detailed planning for deployment and maintenance prepares for monitoring and future enhancements after launch.
Sprint planning practices that work:
A 6-month roadmap for a B2B SaaS platform might look like this: sprints 1–3 deliver core tenant onboarding and authentication. Sprints 4–6 deliver the primary workflow engine. Sprints 7–9 cover integrations and reporting. Final sprints handle performance optimization and a project plan for pilot launch.
Balancing short-term feature delivery with long-term architectural integrity requires discipline. Every sprint should leave the codebase healthier, not just bigger.
TVL IT Solutions coordinates across time zones – for example, an India-based development team with US or EU product owners – using daily standups, asynchronous updates via Slack, and weekly sprint demos. This cadence keeps everyone aligned without requiring midnight meetings.
Development and implementation is where coding transforms designs into functional software. The day-to-day software development process follows a predictable rhythm:
Quality assurance should begin early and include automated testing and peer reviews. Testing should begin as soon as something is usable enough. Defects discovered during development are typically measured in hours to fix, while defects caught in production can take days or weeks.
Secure coding practices include input validation, parameterized queries to prevent SQL injection, secrets management for API keys, and static code analysis integrated into the CI pipeline. Automated testing and continuous integration help catch defects early and reduce costs later.
TVL IT Solutions uses different tech stacks for different domains: Node.js + React for web applications, Unity for game development, Python for AI/ML services, and Swift/Kotlin for native mobile. The choice of programming languages depends on project requirements, not developer preference.
Vignette: In a 2025 fintech project, test-driven development caught a billing miscalculation where rounding logic applied tax before discount instead of after. The bug was fixed in under an hour because the failing unit test pinpointed the exact function. Without TDD, this would have reached production and caused financial discrepancies.
Integration is often the riskiest part of building custom software. Connecting to legacy systems, customer relationship management platforms like Salesforce, ERPs like Microsoft Dynamics, payment gateways, or logistics carriers introduces variables the development team does not control.
Best practices for seamless integration:
Custom software integrates seamlessly with existing systems when integration is treated as a first-class concern. Custom software allows for seamless integration with existing systems, and it provides complete control over features and security.
Example: In 2024, a team integrated a custom order-management system with an existing SAP ERP and a third-party shipping API. Challenges included API versioning mismatches, latency spikes during peak sync, and inconsistent address formats across regions. The mitigation: sequence diagrams documented every flow, and a dedicated integration test suite flagged breaking changes before they reached staging.
TVL IT Solutions documents integration flows using sequence diagrams and guards against external service changes with automated integration testing.
Quality assurance is an end-to-end practice, not a final checkpoint. Testing is an ongoing process throughout the development lifecycle, and quality assurance consumes roughly 30% of overall development effort in well-run projects.
The testing pyramid provides the structure:
Planning test environments that mirror production matters. A staging environment with anonymized data ensures that performance testing and security testing reflect real conditions, not idealized ones.
Automated testing tools can significantly enhance testing efficiency, but they do not replace human judgment. Exploratory testing catches usability issues and edge cases that scripted tests miss.
TVL IT Solutions pairs QA engineers with developers within each sprint, using test case management tools and defect triage meetings. This embedded approach means quality assurance practices run continuously, not in a frantic burst before release.
Inquire about the vendor’s quality assurance and testing processes before engaging any software provider. The answer reveals whether QA is embedded in their culture or bolted on as an afterthought. When evaluating a custom software development company, testing discipline is one of the strongest indicators of delivery reliability.
Each testing layer serves a distinct purpose in the software testing strategy:
Security testing includes penetration testing and vulnerability assessments layered on top of functional validation. This is where security vulnerabilities get identified before attackers do.
Example: A regression test suite for a multi-tenant SaaS onboarding flow caught a role-permission bug in early 2025. A new feature inadvertently granted admin-level access to standard users during the first login. The automated suite flagged the inconsistency before the release reached staging.
TVL IT Solutions blends manual exploratory testing with automated suites using tools like Selenium, Cypress, and Playwright. The balance between speed and depth shifts depending on the module’s risk profile – payment flows get more manual scrutiny, while CRUD screens lean on automation.
User acceptance testing is the phase where business stakeholders and pilot users verify that the custom software actually meets real-world business goals and objectives. It is not a repeat of QA – it is a validation that the software solution delivers the outcomes the organization funded.
Steps to run effective UAT:
Customer feedback enhances user acceptance testing outcomes. Feedback prioritizes features based on customer needs, and customer feedback identifies bugs and improves software quality that automated tests overlook.
Example: In a 2025 UAT round for a custom HR software solution, HR managers, recruiters, and finance staff tested recruitment-to-payroll workflows. The finance team discovered that the payroll export format did not match their accounting system’s import template – a gap that requirements documents had missed but real users caught immediately.
TVL IT Solutions supports remote UAT for global clients, providing UAT support windows that match client time zones so feedback loops stay tight.
Non-functional testing validates that enterprise-ready custom software can scale, stay secure, and remain stable under real-world usage patterns. Scalability enhances user experience by maintaining performance under load – and non-functional testing proves it.
TVL IT Solutions uses results from performance testing to refine architecture – adding caching layers, tuning database queries, tightening access controls. These refinements feed directly back into the sprint backlog.
Modern software development treats non-functional testing as a continuous concern. The performance envelope of a system changes with every release, and only continuous testing keeps it in check.
DevSecOps integrates development, operations, and security throughout the pipeline. Instead of treating security and ops as separate phases, they run as continuous integration checkpoints in every build.
A typical CI/CD pipeline looks like this:
Automated gates reduce human error and shorten release cycles. A build that fails a security scan or test suite does not proceed. This discipline ensures that custom solutions reach production in a known-good state.
Example: A TVL IT Solutions client moved from quarterly releases in 2022 to weekly deployments by 2025 after implementing a mature CI/CD pipeline. The shift did not require hiring more engineers – it required better automation, and the result was faster delivery with fewer production incidents.
Continuous integration is not just a tooling choice. It is the operational backbone of any modern software development process, and it transforms how teams ship custom software products.
Deployment and launch consist of releasing software into production and configuring servers, but the strategy behind that release determines how much risk the organization absorbs.
Common deployment strategies:
Infrastructure choices – cloud versus on-premise versus hybrid – affect deployment automation, rollback capabilities, and disaster recovery planning.
Data migration requires separate planning: ETL jobs map old data formats to new schemas, backups run before cutover, and parallel systems operate briefly to validate data integrity.
Example: In 2024, a new logistics portal rolled out to one region first. The team monitored error rates, latency, and user feedback for two weeks before enabling additional regions. This phased approach caught a timezone-handling bug that only manifested in the second region’s locale settings.
TVL IT Solutions prepares runbooks and deployment checklists for client operations teams, ensuring deployments can be repeated confidently without relying on individual engineers.
What happens immediately after launch often determines long-term adoption. The hypercare period – typically the first 2–4 weeks – involves elevated monitoring and rapid response for high-priority issues.
Post-launch practices include:
Maintenance and support monitor performance, release updates, and scale features based on user feedback. This is where the software begins its evolution from “project” to “product.”
Example: During the first week after launching a B2B integration platform, the team detected a spike in API errors affecting one downstream system. Proactive monitoring identified the root cause – a rate limit change by the external vendor – within 90 minutes. A fix deployed the same day, limiting customer impact to fewer than 50 requests.
TVL IT Solutions acts as an extended operations team for offshore clients, handling production support within agreed service windows and escalating critical issues through defined paths.
Custom software is a long-term asset. Software applications typically remain in active use for 8–12 years before being rewritten, and maintenance constitutes 60–80% of total lifecycle cost.
Four types of ongoing maintenance define the work:
Annual maintenance investments typically equal 15-20% of initial development cost. Annual maintenance costs typically equal 15-20% of initial development costs, making it essential to budget for ongoing evolution from the start.
Industry data shows custom software development costs can range from thousands to hundreds of thousands of dollars depending on scope, and the average cost for a new feature in medium-sized systems is around $100,000. These figures reinforce why a quarterly or biannual roadmap review – reprioritizing features based on real usage analytics – delivers the best return.
Example: A logistics platform originally built in 2021 added route-optimization AI models in 2024 without needing a full rewrite, because the original architecture supported modular extension. Emerging technologies like AI and ML integrate smoothly when the foundation is designed for change.
TVL IT Solutions structures long-term partnerships with flexibleengagement models – dedicated team, time and material, or hybrid – focused on continuous improvement rather than one-off delivery.
Security by design means considering protection from requirements through architecture, coding, testing, and operations – not bolting it on before launch.
Practical measures include:
Collaboration with client security teams covers policies, audit requirements, and periodic penetration testing. Custom software provides a competitive advantage through unique features, and enhanced security is one of the most valuable.
Example: Building a healthcare custom software web portal in 2025 required compliance with HIPAA in the US and local data residency laws in the EU. Design choices – including data partitioning by region and end-to-end encryption – were driven by regulatory requirements identified during discovery, not retrofitted after development.
TVL IT Solutions keeps its teams current with security best practices and integrates automated security testing into CI/CD pipelines for every project. Business process automation features are only as valuable as the security protecting them.
Performance requirements should be captured as concrete targets: response times under 300ms for key APIs, ability to handle specific peak loads, and throughput benchmarks based on realistic growth projections.
Design patterns that support scalability:
Capacity planning should rely on monitoring data and historical usage, not guesswork. Cloud platforms make elastic scaling possible, but only if the application architecture supports it.
Mini case study: An e-commerce client’s system handled a major marketing campaign in 2025 without degradation because proper load testing identified a database bottleneck weeks earlier. The team added a caching layer and tuned queries. On campaign day, the system scaled smoothly under three times normal traffic.
TVL IT Solutions treats performance as a continuous concern, not a one-time optimization just before launch. Every sprint includes performance regression checks to catch degradation early.
Collaborating with an offshore custom software development partner like TVL IT Solutions extends in-house teams with specialized technical expertise in areas like AI/ML, Salesforce, Microsoft Dynamics, and mobile app development. Effective communication and collaboration are vital for a successful partnership.
Communication patterns that make offshore work effective:
Common concerns and their mitigations:
Engagement models provide flexibility. Fixed-price contracts provide cost predictability for clients. Time and materials contracts allow flexibility in project scope. Dedicated team contracts offer ongoing development support. The right development partner matches the model to the project context.
Successful project management requires defining clear roles and responsibilities among team members. Technical skills matter, but governance and transparency matter more in offshore partnerships. For guidance on selecting the right partner, see How to Choose a Custom Software Development Company.
Good governance prevents drift. The structures vary by organization size:
Documentation throughout the software development lifecycle is not bureaucracy – it is insurance:
Structured knowledge transfer – recorded walkthroughs, code handovers, admin training – prevents vendor lock-in and ensures internal teams can operate the system independently.
TVL IT Solutions provides comprehensive documentation and training at each major milestone, not just at project end. This approach ensures that if the client wants to bring operations in-house or switch partners, they can do so without losing institutional knowledge.
Custom software development offers long-term value only when the knowledge stays with the organization, not locked in a vendor’s head.
Every custom software development project faces recurring risks. Here is a concise checklist:
Anonymized example: A mid-market retailer in 2023 skipped discovery and jumped straight into development of an inventory management system. Six months in, the team discovered the existing ERP’s API could not support real-time sync. The result: three months of rework and a delayed launch. Robust discovery would have surfaced this in week two.
An experienced development partner like TVL IT Solutions spots early warning signs – architecture drift, quality erosion, requirement ambiguity – and escalates before they become expensive problems. Custom software development pros include this vigilance as part of the delivery model.
The process described in this guide is not theoretical. Here is how TVL IT Solutions applies it across domains:
A disciplined yet flexible software development process – spanning discovery, design, development, testing, deployment, and evolution – transforms business ideas into reliable, scalable custom software solutions. The difference between a project that delivers and one that derails traces back to process discipline far more than technology choices.
Aligning the software development process with business goals and business needs is more critical than any individual framework or tool. When that alignment holds, custom software becomes a compounding asset – improving operational efficiency, enabling business process automation, and adapting to emerging technologies year after year.
TVL IT Solutions serves as a long-term custom software development partner, guiding clients through the full lifecycle with security-first, cloud-ready, and scalable architectures. Whether you need a dedicated team for a startup launch or enterprise-grade solutions for complex business processes, the process outlined here is how results happen.
Your next steps:
The right process, the right partner, and clear business goals are what separate custom software that delivers lasting value from projects that become cautionary tales.
The custom software development process is a structured lifecycle covering business planning, discovery, requirements, architecture, design, development, testing, deployment, support, and continuous improvement.
The process includes aligning business goals, choosing an SDLC model, discovery, requirements gathering, architecture, UX/UI design, agile planning, development, integration, QA, UAT, deployment, post-launch support, and maintenance.
Discovery identifies business requirements, existing-system dependencies, regulatory constraints, data migration challenges, risks, and technical feasibility before development begins.
Security should be embedded throughout the lifecycle through threat modeling, access controls, encryption, secrets management, dependency patching, audit logging, and continuous security testing.
Post-launch work includes monitoring, incident management, maintenance, security updates, performance optimization, feature enhancements, and continuous evolution based on user feedback and business needs.
At TVL IT Solutions, we specialize in delivering scalable, secure, and custom software development services tailored to your unique business needs. Whether you’re a startup or an enterprise, our team is ready to turn your vision into reality.
Get Started Now